EXPLORE RESOURCES

Certificate Authority Articles

6 Articles

Common Pitfalls When Implementing Private CAs

Standing up a private Certificate Authority is a well-documented process, discussed throughout this series, but the gap between a technically functioning private CA and a genuinely well-run one is where most organizations actually struggle. This article covers the specific pitfalls that recur most often during private CA implementation, drawn from patterns discussed across this series\’ coverage of internal PKI.

Cost-Benefit Analysis: In-House CA vs Managed PKI Services

Deciding whether to build and run a private CA internally or adopt a managed PKI service is one of the more consequential infrastructure decisions a growing organization will make, and it deserves a genuine cost-benefit comparison rather than a default assumption in either direction. This article walks through that comparison directly.

Internal vs External Certificates: Strategy Guide

One of the most consequential early decisions in any certificate strategy is a deceptively simple one: which certificates should come from a public CA, and which should come from an internal private CA instead. Getting this wrong in either direction creates real problems, unnecessary cost and complexity on one side, or unnecessary risk and compatibility headaches on the other. This article lays out a practical framework for making that call correctly and consistently.

Comparing Public CAs: DigiCert, Sectigo, GlobalSign, and More

Choosing among public Certificate Authorities involves more than comparing sticker prices, since each major CA differentiates itself through validation options, automation support, support quality, and specific enterprise features. This article compares several of the major players in the space to help frame that decision, without treating any single vendor as universally the right answer.

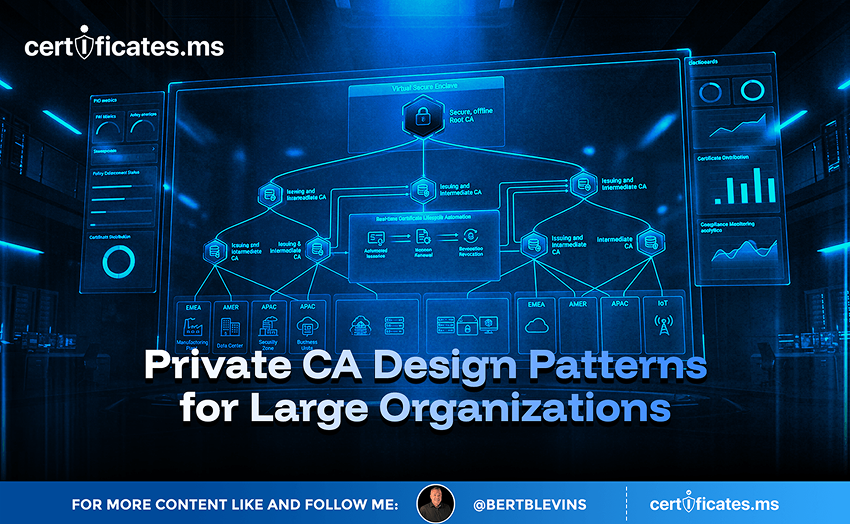
Private CA Design Patterns for Large Organizations

A large organization\’s internal certificate needs rarely fit neatly into a single, simple CA structure. Different business units have different risk profiles, different geographic regions face different regulatory requirements, and different categories of identity, from employee laptops to AI agents, need meaningfully different issuance policies. This article covers the design patterns large organizations actually use to structure a private CA that can serve all of this coherently, building on the foundational internal CA concepts covered earlier in this series.

Root Certificates vs Intermediate Certificates – Key Differences

Root and intermediate certificates work together so seamlessly in practice that the distinction between them often gets glossed over, even by people who work with certificates regularly. Understanding exactly how they differ, and why the distinction exists at all, is essential to understanding how the entire trust ecosystem holds together. This article lays out the key differences and the reasoning behind them.