EXPLORE RESOURCES

PKI Articles

31 Articles

Replacing Passwords with Certificate-Based SSO

Single sign-on has already reduced password fatigue considerably by letting users authenticate once and access many connected applications, but most SSO implementations still rely on a password at that initial authentication step, preserving the exact weakness SSO was meant to reduce. Certificate-based SSO removes that remaining password dependency entirely. This article covers how this works and what it takes to deploy well.

Teaching Certificate Concepts: 101, 201, 301 Curriculum Outline

This series has, across its full run, effectively built out a complete certificate education curriculum organized around exactly this progression: foundational concepts, intermediate operational depth, and advanced architectural mastery. This article pulls that structure together explicitly, giving trainers and team leads a concrete outline for teaching certificate concepts in a properly sequenced way, referencing where each topic is covered in more depth elsewhere in this series.

Smart Card and FIDO2 Integration with Certificates

Smart cards and FIDO2 security keys represent two generations of hardware-backed authentication, both built around the same core idea of keeping a private key physically isolated from the device attempting to authenticate. Understanding how each integrates with certificate-based authentication, and where they overlap and diverge, matters for any organization designing strong, phishing-resistant authentication. This article covers both technologies and how they fit alongside the certificate concepts covered throughout this series.

Debugging Certificate Chain Issues in Production

Chain of trust concepts, covered earlier in this series, are straightforward to explain in the abstract, but diagnosing a real chain-related failure in a live production environment, often under real time pressure with customers actively affected, requires a systematic approach rather than guesswork. This article walks through exactly how to debug certificate chain issues methodically when they surface in production.

Scripting Certificate Requests with REST APIs

Beneath every ACME client, CLM platform, and CI/CD certificate integration discussed throughout this series sits the same fundamental building block: a REST API call requesting a certificate. Understanding how to script these requests directly gives developers and administrators a level of flexibility that pre-built tools sometimes cannot match. This article covers the practical patterns for scripting certificate requests against REST-based CA and CLM APIs.

Using Certificates for API Authentication and Authorization

API keys and bearer tokens dominate most API authentication conversations, largely because they are simple to implement. Certificates offer a genuinely stronger alternative for a meaningful subset of API use cases, particularly where the stakes are high enough to justify the additional setup effort. This article covers how certificate-based API authentication actually works and where it earns its added complexity.

Certificate Revocation in Cloud Environments (AWS, Azure, GCP)

Revocation, covered conceptually elsewhere in this series, takes on distinct practical characteristics inside each major cloud provider\’s ecosystem, since AWS, Azure, and Google Cloud each handle certificate issuance and revocation through their own managed services with their own specific mechanics and limitations. This article covers what revocation actually looks like across these three platforms.

HSMs and Hardware Security Modules for Certificate Protection

Hardware security modules occupy a distinct tier in the private key protection hierarchy discussed elsewhere in this series, offering a level of assurance software-based storage simply cannot match for an organization\’s most sensitive keys. This article looks specifically at what HSMs are, how they work, and where the investment genuinely pays off.

Certificate Misconfiguration Disasters: Lessons Learned

The certificate world\’s cautionary tales tend to follow recognizable patterns, and studying them is often more instructive than any amount of abstract best-practice guidance. This article walks through the categories of certificate misconfiguration that have caused genuine, well-documented incidents across the industry, and the specific lessons each one teaches.

PowerShell Scripts for Bulk Certificate Operations

Windows-centric environments often accumulate certificates across dozens or hundreds of servers, and reaching into each machine\’s certificate store individually to check, renew, or clean up certificates does not scale past a handful of systems. PowerShell offers a genuinely powerful toolkit for handling these operations in bulk, and this article covers the practical patterns for using it effectively.

Zero Trust Architecture and Certificate-Based Access

Zero trust has become one of the most widely referenced concepts in enterprise security, and also one of the most loosely defined in casual conversation. Stripped of marketing language, zero trust rests on a fairly simple principle: never trust a connection by default, verify it explicitly every time, regardless of whether it originates inside or outside the traditional network perimeter. Certificates are one of the most concrete, practical tools for making that principle actually enforceable rather than aspirational. This article covers exactly how the two fit together.

VPN Certificate Authentication: Stronger Than Pre-Shared Keys

Pre-shared keys remain a common way to authenticate VPN connections, largely because they are simple to configure and understand. They are also a genuinely weaker security model than certificate-based authentication, and understanding exactly why is worth walking through directly. This article compares the two approaches and makes the practical case for moving VPN authentication toward certificates.

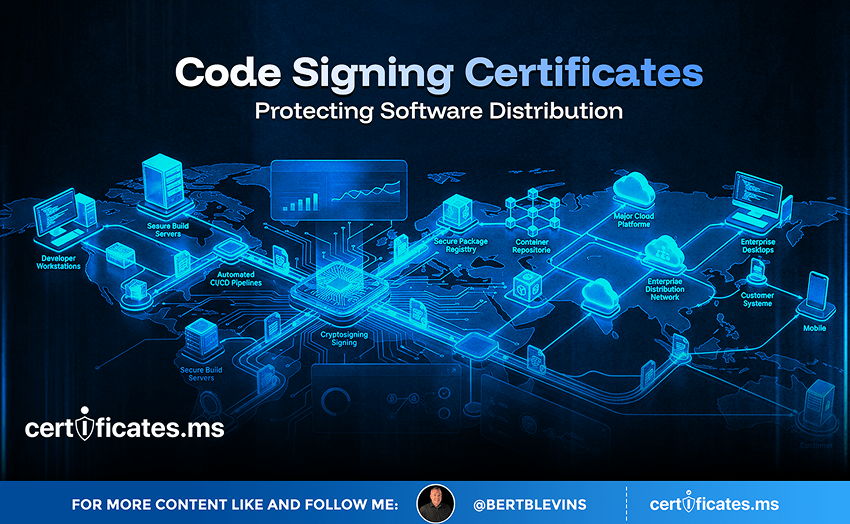
Code Signing Certificates: Protecting Software Distribution

Every time an operating system displays a warning about an unrecognized publisher, or silently allows an application to install without any friction at all, a code signing certificate is somewhere behind that decision. This article covers how code signing actually works, why it matters more than ever given the current software supply chain threat landscape, and what organizations distributing software need to get right.

Quantum-Resistant Certificates: Preparing for Post-Quantum Cryptography

Quantum computing capable of breaking today\’s public key cryptography does not exist yet, but the cryptographic standards designed to survive it already do, and the certificate ecosystem is beginning the long process of adopting them. This article covers what quantum-resistant certificates actually involve, where the industry genuinely stands today, and what organizations should realistically be doing to prepare

Revocation Checking in Browsers and Applications

Revocation exists to invalidate a certificate before its natural expiration, but a revocation mechanism only matters if clients actually check it. This article looks specifically at how browsers and applications handle revocation checking in practice, where the theory of CRLs and OCSP, covered in depth elsewhere in this series, meets the messier reality of what actually happens during a real connection.